(518) 292-4500|sales@logical.net|M-F 8am-5pm · 24/7 SOC
MSP 501 Winner 2025Client Portal →
Free Assessment · No obligation

Find out where you're exposed.

A free, no-obligation vulnerability scan shows you the same external attack surface a bad actor sees, and gives you a prioritized list of what to fix first. Takes about 5 minutes to start.

Scanned from the outside Nothing to install Results in about 48 hours
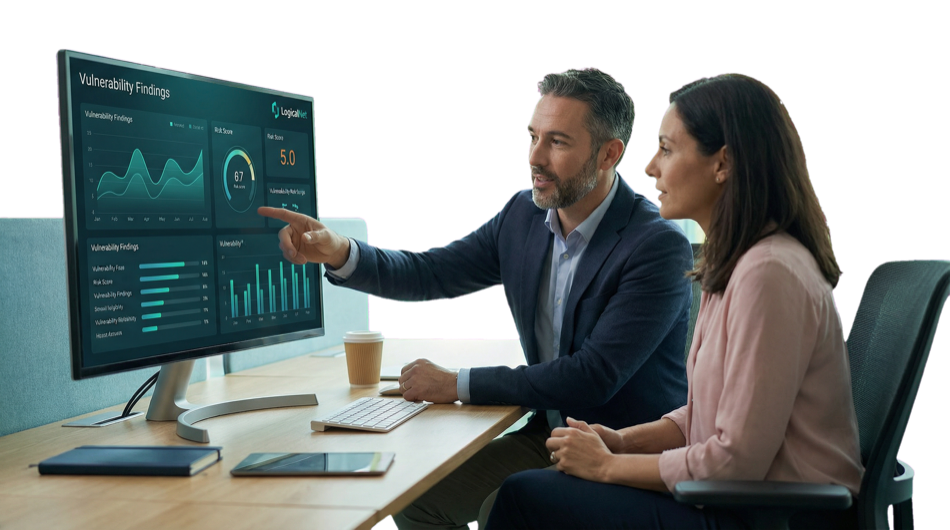
Reviewing the results of a vulnerability scan
5 min
To get started
48 hrs
Typical turnaround
Risk score
Clear, prioritized rating
Fix list
Ranked by what matters
$0
No obligation
How it works

Three steps to knowing your real risk.

No long engagement, no software rollout. Pick a time, we scan from the outside, and you get a plain-language readout with a real engineer to walk you through it.

1

Schedule

Pick a time below and give us your business domain and a few basics. No credentials, no access to your systems, nothing to install or take offline.

About 5 minutes
2

We scan

We map your external attack surface the way an outside attacker would — open ports, exposed services, patch gaps, email and DNS records, all from outside your network.

About 48 hours
3

You get results

A prioritized report plus a 30-minute call with a LogicalNet engineer to walk through what we found and what to fix first. No sales script.

A real conversation
What you get

Not a scanner dump — a plan you can act on.

Raw vulnerability output is noise. You get findings scored by real-world risk, written for both the server room and the boardroom.

Risk Score Report

A single, plain-language rating of your external exposure, so leadership sees where you stand without reading raw scanner output.

Prioritized Vulnerabilities

Every finding ranked by real-world risk and effort to fix — what to close today, what to schedule this month, and what can wait.

External Attack-Surface Map

An inventory of what faces the internet under your name: domains, services, open ports, and systems nobody remembers standing up.

Executive Summary

A one-page brief written for owners and boards, not engineers, the business version of the technical findings.

Remediation Guidance

Specific, concrete steps to close each gap, whether your own team handles it or you bring us in to help.

A Real Conversation

A 30-minute review call with a local engineer to answer questions and talk through next steps. No obligation to buy anything.

What we check

The same doors an attacker rattles.

The scan looks at what the public internet can already see about your organization, the openings that get probed first.

External exposure & open ports

Which services and ports answer from the public internet, including ones nobody remembers turning on.

Missing patches

Internet-facing software running known-vulnerable versions that automated attacks actively scan for.

Email spoofing & DMARC

Whether someone can send email as your domain because SPF, DKIM, and DMARC records aren't set correctly.

Exposed services & entry points

Internet-facing logins, remote-access services, and management interfaces an attacker would try first.

Cloud & Microsoft 365 misconfig

Common tenant settings that leave Microsoft 365 and cloud data more open than they should be.

Website & DNS hygiene

Expiring certificates, weak DNS records, and configuration that quietly leaks more than it should.

Pick a time

A 30-minute intro call is the whole commitment.

Choose a slot that works for you. We'll confirm the details, run the scan, and meet to walk through your results together.

  • A local Capital Region engineer, not a call center
  • We only need your business domain to begin
  • No pressure and no obligation to become a client
Book your assessment

Pick a time that works for you

A 30-minute working session with Tush Nikollaj, our CEO. Video call via Microsoft Teams. No prep needed — bring whatever you already know about your environment and we’ll take it from there.

Open the scheduler
Opens our live scheduling tool · 30-minute intro call · no obligation
Questions

Before you book a time.

Is it really free?

Yes. The scan and the review call cost nothing and come with no obligation. It's how we introduce ourselves — you get a clear picture of your risk whether or not you ever become a client.

Is the scan safe and non-intrusive?

Yes. We look at your external attack surface from the outside, the same public-facing view an attacker has. Nothing is installed, nothing is taken offline, and we don't touch the inside of your network.

What do I need to provide?

Your business domain and a few basics about your organization. That's enough to start. No credentials, no access to your systems, and no software to deploy.

What happens after the scan?

You get a prioritized report and a 30-minute call with a local engineer to walk through it. If you want help closing the gaps, we'll scope the work. If not, the report is yours to keep.

How long does it take?

Most scans are back within about 48 hours. The review call is scheduled at a time that works for you — starting one takes about 5 minutes.
See what an attacker sees — before they do.

Start your free vulnerability scan today. Clear results, a prioritized fix list, and a real engineer to talk it through. No obligation.